 Fynchat
How do we protect your data?
An explanation of the security and privacy measures we apply to protect your account and your customers.
Data isolation (Multi-tenancy)
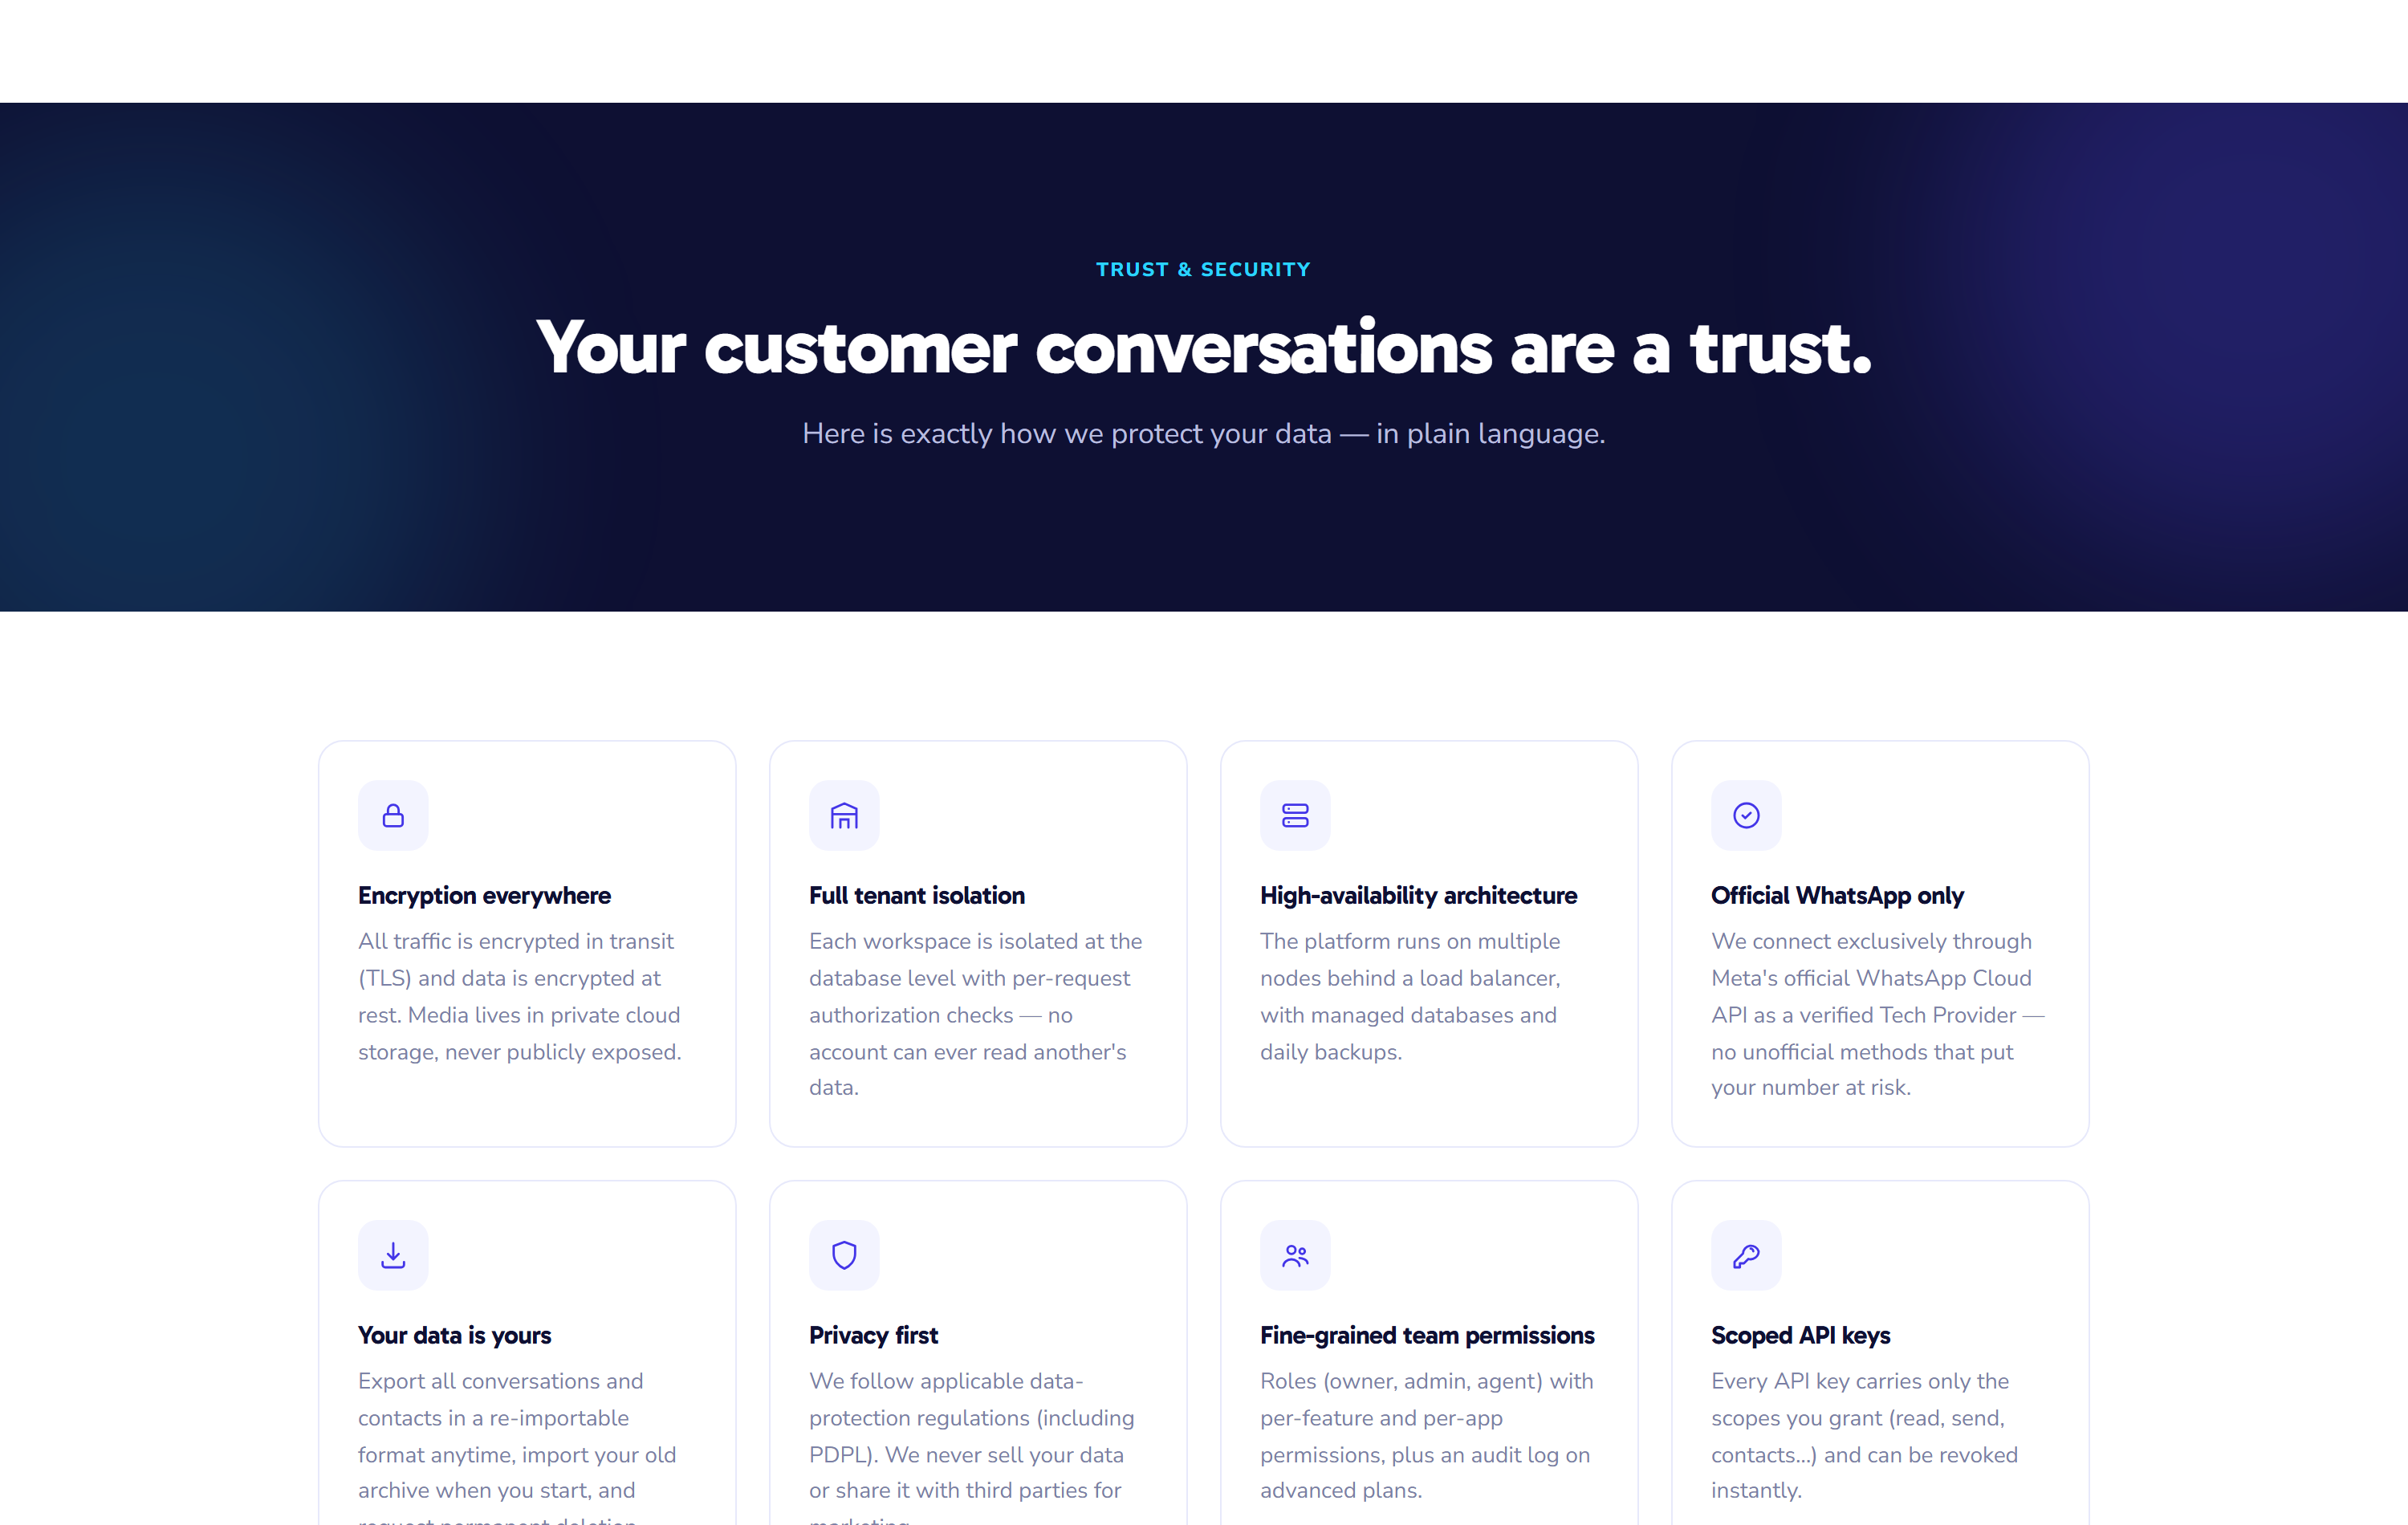
Each customer account in Fynchat is fully isolated from every other one at the technical level:
- Every database query is automatically filtered by your account
- It is impossible for a user in company A to reach company B's data by tampering with the URL or the API
- We test this isolation automatically with every update
Encryption
- Data in transit is always encrypted over a secure connection (HTTPS).
- Stored data is encrypted at rest.
- Passwords are never stored as typed, only in a one-way protected form that cannot be recovered.
- Integration keys and access tokens are stored encrypted and never shown in logs.
Access
- Your account is protected by a strong password + email confirmation
- You can turn on two-factor authentication (2FA) for your account from the two-factor page, using an authenticator app such as Google Authenticator
- We log every sign-in with IP and time
- If we detect suspicious activity, we terminate the session immediately and send you an alert
Backups
- Daily at midnight (UTC)
- Encrypted + stored in a separate location
- 30-day retention for backups
- Recovery: less than 4 hours (RTO), less than one hour of data loss (RPO)
What we log (Logs)
We log only the necessary information:
- ✅ Sign-in and sign-out events
- ✅ Account settings changes
- ✅ Campaign sends
- ✅ System errors
We do not log:
- ❌ Passwords
- ❌ Message content (except to display it in the inbox)
- ❌ Credit card information (we use specialized payment gateways)
Compliance
- 🇸🇦 Saudi Personal Data Protection Law (PDPL) — compliant
- 🇪🇺 GDPR — compliant (for customers who have European customers)
- 🌍 Meta Data Use Policy — adherent
Review:
Data sharing
We do not sell your data to anyone. We share it only with:
| Party | Why |
|---|---|
| Meta (WhatsApp) | To send messages via the official API |
| AWS | For hosting and sending emails |
| Government authorities | Only under a valid court order |
Your rights
Under the PDPL and GDPR, you have the right to:
- Access your data → request it at [email protected]
- Correction → via account settings
- Deletion → request full deletion of your account
- Portability → we export your data in JSON / CSV format
We commit to responding within 30 days.
Reporting a breach
If you notice anything suspicious (an unfamiliar sign-in, unusual messages, etc.):
- Change your password immediately
- Report it to [email protected]
- We will investigate and respond within 4 hours
Vulnerability Disclosure Program
We value security researchers and welcome responsible reports. Participation is subject to these terms:
Prior authorization
- Written permission from us is required before any security testing begins. Send your request to [email protected] with your real name, email, country, what you intend to test and how, and the account you will test on. We review the request and either approve it with a defined scope and time window, or decline it. The decision is ours alone, and nothing may begin before our written reply.
- Any testing without permission is unauthorized activity, is not eligible for any reward, and we reserve the right to take appropriate action.
- Accidental discovery during normal use is exempt, provided you stop immediately and report in good faith.
Eligibility
- Only the first reporter of a vulnerability; duplicates are not eligible.
- Testing must be on an account you created yourself, with your own real email and phone number. Temporary emails or fake numbers mean rejection.
What counts
- A real, demonstrated impact on customer data or our servers, not a theoretical risk.
Out of scope (not rewarded)
- Automated scanner reports, and reports without reproduction steps.
- Missing security headers, cookie settings, or email records.
- Clickjacking on pages with no sensitive action.
- Denial of service, load or flooding tests.
- Password guessing and rate-limit testing.
- Social engineering, or targeting our staff.
- Vulnerabilities in third-party services such as Meta or payment providers.
How to report
- A clear report in Arabic or English: the affected page or path, numbered reproduction steps, the actual impact, and a short proof.
- Through the email above only. Reports via chat or social media are not accepted.
Conduct (a breach voids any reward)
- Stop at proof: do not extract, read, keep or use any data.
- No passwords, keys or customer data in the report or anywhere else.
- No publication or disclosure to anyone before the fix and our written permission.
- Any demand for payment or threat to publish means immediate disqualification.
Reward
- Entirely at our discretion in type and amount, and may be a thank-you or public credit with no payment.
- Paid only after the fix is verified, to an identity-verified individual, through an official payment channel.